Roles and permissions
Define what users can do.
A role is a set of permissions. Users receive a role on a group (or on a single machine shared with them): the role applies to the machines of that group and of its subgroups.
Open Admin › Roles.
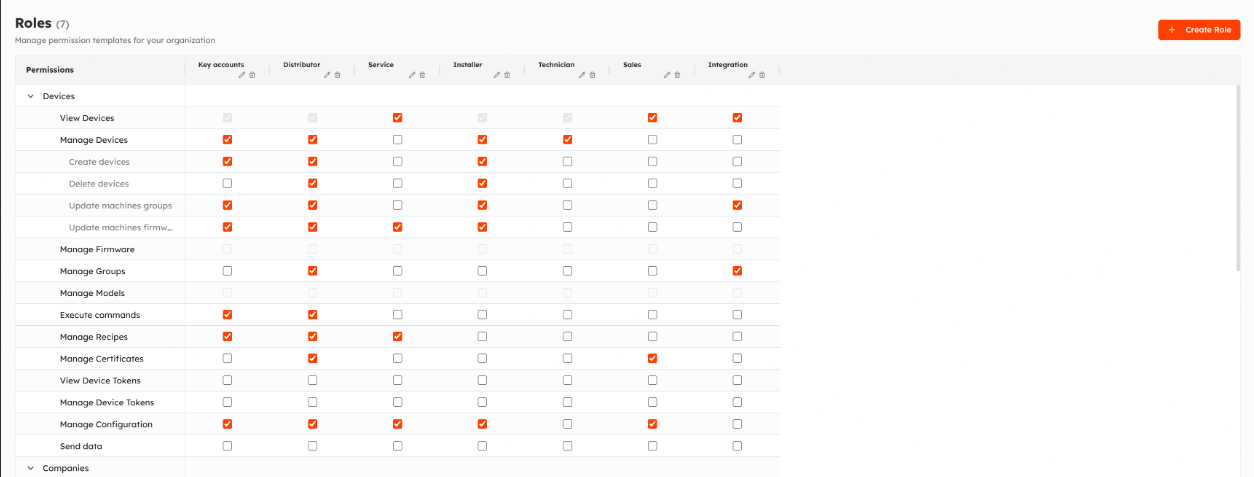
The page is a matrix: one column per role, one row per permission, grouped by category (devices, companies, users, configuration levels, subscriptions…). Create Role adds a role; each role can be renamed or deleted. Permissions reserved to administrators are locked.
Main permissions
| Permission | Allows |
|---|---|
| View Devices | See machines and their data |
| Manage Devices | Edit machines; includes creating, deleting, changing group and updating firmware |
| Manage Groups | Create and edit groups |
| Execute commands | Run commands and actions |
| Manage Recipes | Edit recipes and send cookbooks |
| Manage Certificates | Get certificates and pairing codes for machines |
| Manage Configuration | Read and write parameters |
| View / Manage Device Tokens | See and manage device tokens |
| Send data | Send machine data to Things5 through the HTTP API |
| View / Manage Users | See and manage users |
| Manage plans, Manage machine plans | See Plans |
Configuration levels
Each parameter has an access level from 1 to 5, set on the firmware. For each level a role can hide the parameters, allow to read them, or allow to write them. This way, for example, a technician can change parameters that an end user only sees.
Assignable roles
Assignable Roles lists the roles that users with this role can give to others when they invite users or share machines.
How permissions add up
Permissions are cumulative: a role on a parent group extends to its subgroups and cannot be restricted by a role on a child group; when a user has several roles, the broadest one wins.
The full list of permissions, with their API names, is in Permissions.
Video
Watch the video on YouTube. It shows the previous version of the interface: an updated video is coming.
Updated 9 days ago